Your app stays yours.
Letting an AI click around your product is a real decision. Here is exactly what Framefly can see, what it can never do, and what it keeps.
The AI never sees a password.
Secrets are encrypted in a vault and only decrypted inside the short-lived worker that runs your shoot. The model writes a placeholder; the browser fills in the real value. Logging in is never filmed: recording starts after you're signed in.
AES-256-GCM, one data key per workspace, held by AWS KMS in Frankfurt.
Plans the next action with a placeholder, never the value.
fill("#password", {{secret.password}})Swaps the placeholder at the last moment, in memory. Never written to logs.
Receives a normal sign-in. Each decryption is recorded in your audit log.
Secrets of an app with no render for 90 days are purged. Ephemeral mode deletes them after every render.
Who decrypted what, when, and for which render. Filter it by secrets, renders, guardrails, members or API.
Once saved, nobody can read a secret back, you included. You can only replace or delete it.
Three checks on every action.
Before the browser runs a click, a form fill or a navigation, the action passes three layers. If the agent hits more than five blocks in one exploration, it stops, keeps your credit and tells you.
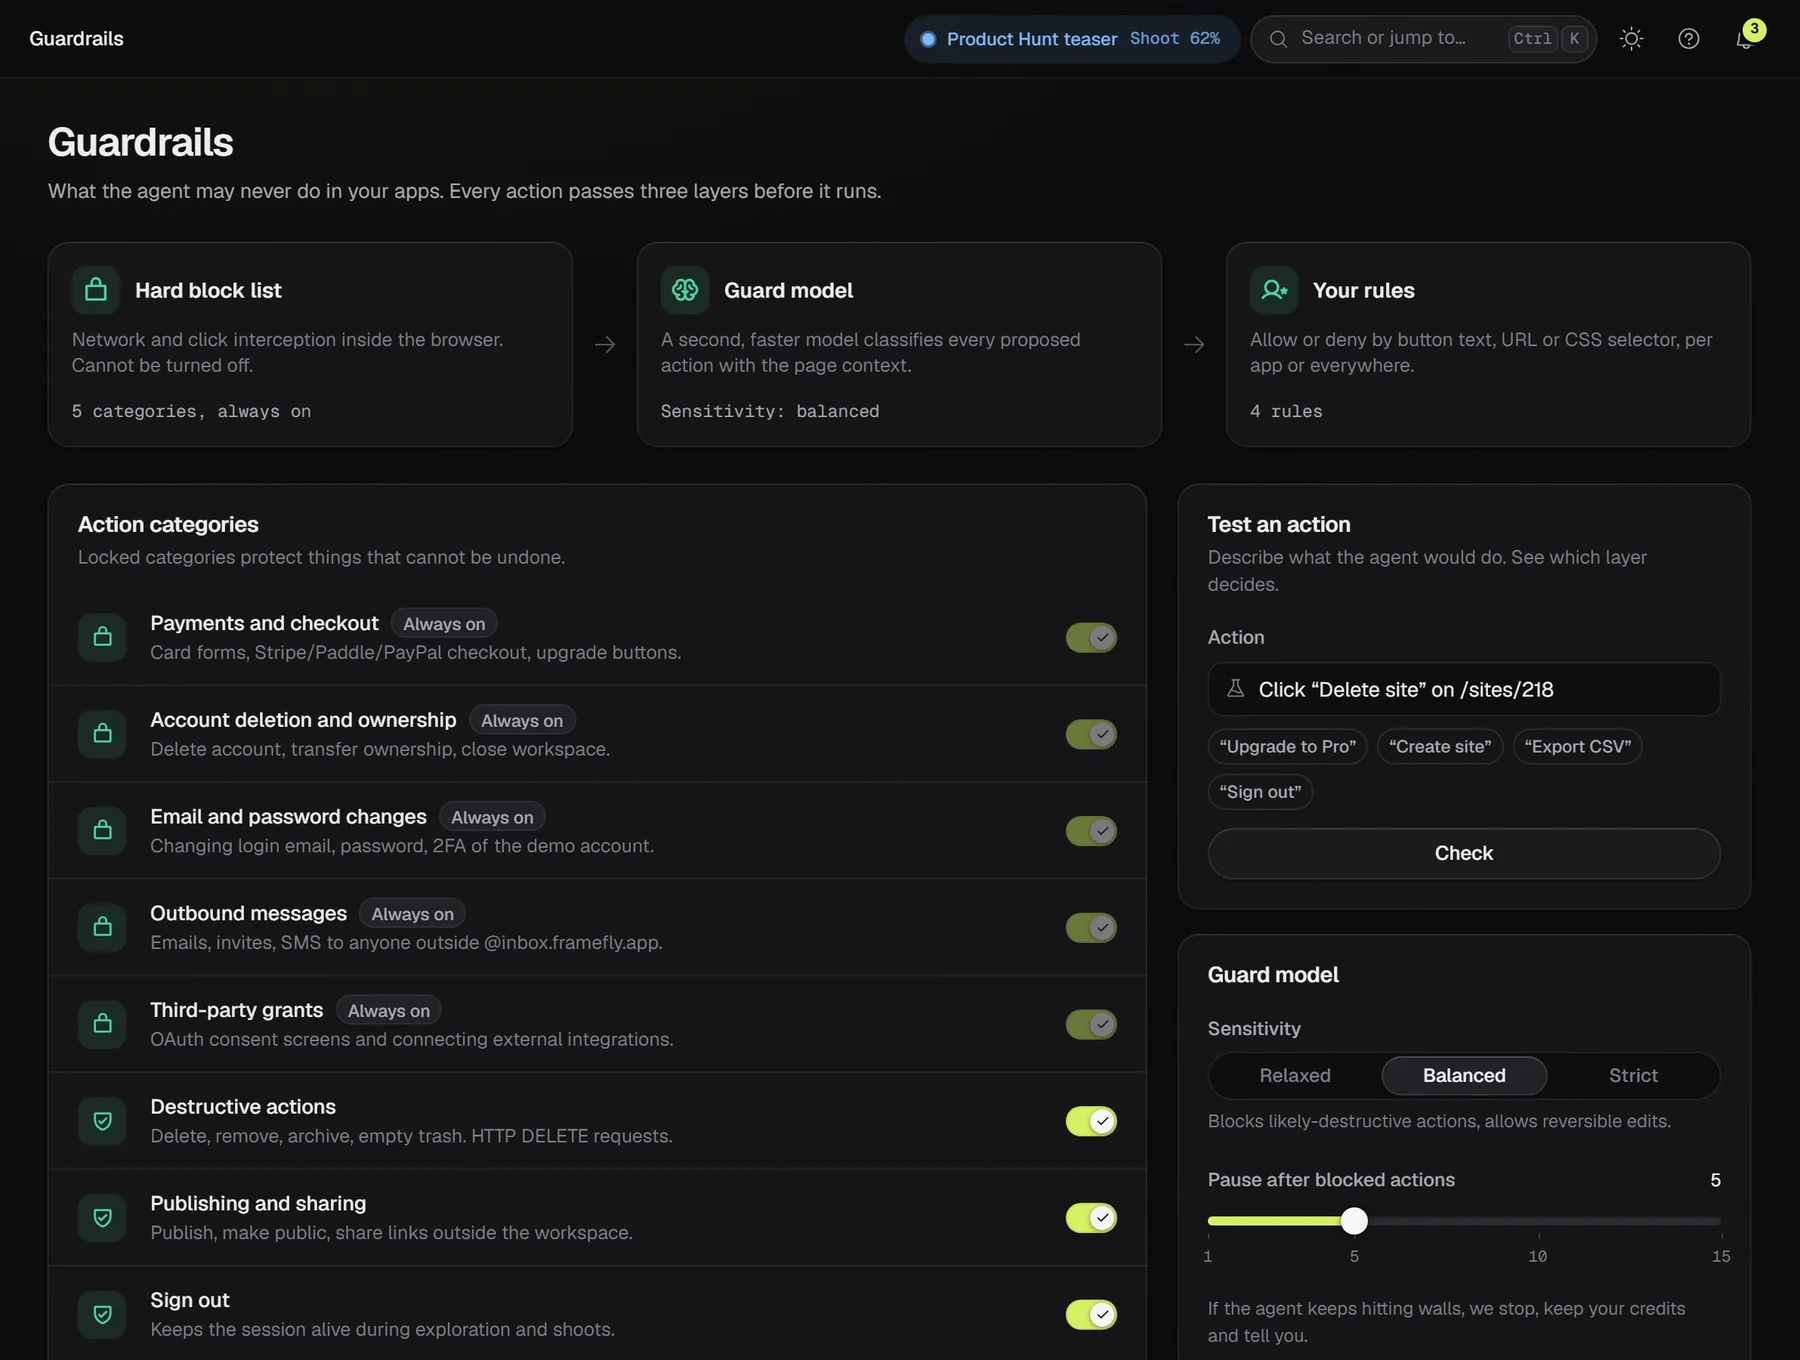
Inside the browser: payment domains are cut off at the network, DELETE requests are refused unless you allowlist them, and clicks on destructive words are stopped in ten languages.
A second, faster model reads each proposed action with the page around it. Anything risky is blocked unless you allowed it.
Allow or deny by URL, CSS selector or button text, for one app or for all of them.
Always blocked, even if you allow it
If your app sits behind Cloudflare or a firewall, Framefly doesn't try to sneak past it. It uses fixed outgoing IPs and signs every request with an X-Framefly-Agent header, so you can allow it in one rule.
What we keep, and for how long.
Framefly is hosted in the EU. For the data visible in your demo accounts, Framefly is your processor under the GDPR and a data processing agreement is available. You can export or delete everything at any time.
These are the defaults. Each one can be shortened in the app.
- Raw captures and takes
- 30 days
- Exploration screenshots
- 30 days
- Codes received in the agent inbox
- 24 hours
- Secrets of an idle app
- 90 days
- App map
- while connected
- Delivered videos
- until you delete
- Share page analytics
- 13 months, no personal data
Labeled as AI, the way the law asks.
Since August 2, 2026, article 50 of the EU AI Act requires AI-generated media to be marked. Framefly does it by default, so your video is compliant without you thinking about it.
- Content Credentials (C2PA) and XMP metadata in every exported file
- One line on the end card, "Voice generated with AI", styled to match your brand
- A corner label whenever an AI presenter is on screen. It can't be switched off.
- Consent first. Cloning a voice or a face starts with you reading a random phrase aloud, and only works for yourself.
Who helps us run it.
The services Framefly plans to rely on at launch. The final list is published here before launch day, and you'll be told before a new one is added.
| Service | What for | Where |
|---|---|---|
| Anthropic | Exploration, planning and the guard model | US, with standard contractual clauses |
| Voice and music provider | Voice-over and music, chosen after a blind listening test | Published before launch |
| Presenter provider | AI presenter, beta | Published before launch |
| Hetzner | Exploration and shoot workers | EU, Germany |
| AWS | Rendering and key management | EU, Frankfurt |
| Cloudflare | Video storage and delivery | EU jurisdiction |
| Stripe | Payments | EU and US |
| Postmark | Transactional email | US, with standard contractual clauses |
Found a security issue? Write to support@framefly.app with "Security" in the subject. You'll get a reply within two working days.
Questions about your setup?
Beta testers go through the connection with the maker, one to one.